 |
plc.myforum.ro
PLCs users www.plc.myforum.ro!
|
| View previous topic :: View next topic |
| Author |
Message |
AnteSavilt
Member 2
Joined: 13 Feb 2018
Posts: 264
Location: Croatia
|
 Posted: 07/01/2022 08:30 Post subject: Log4J Vulnerability |
 |
|
Log4J Vulnerability
https://support.industry.siemens.com/cs/document/109805593/
How to secure your system
1. On your computer, go to assets.bpcloudapps.siemens.com
2. Click Log in/Sign up
3. Enter your Account email and password
4. Click Log In
5. Go to Sites.
6. Select the site with the Connect X200/300 device
7. Select the device.
8. Go to Applications
9. Click Update > confirm with Update.
For the X200: Building Operator Discovery Distribution v3.0.30
For the X300: Building Operator Discovery Distribution v3.0.29
How to verify that your system is protected
• (you are still logged in Asset Portal web site)
• Go to Services and verify that the status of your applications is healthy and are updated with the following versions:
For the X200
o Haystack Cloud Connector 3.0.1
o Building Operator Discovery 1.0.4
o GW-Cloud-Connector 2.5.12
For the X300
o Haystack Cloud Connector 3.0.1
o Building Operator Discovery 1.0.4
Devices Application User Guide
https://sid.siemens.com/r/A6V12050067/17771235723___en-US_17633248267
https://sid.siemens.com/r/A6V12050067/17771235723___en-US_17633351691
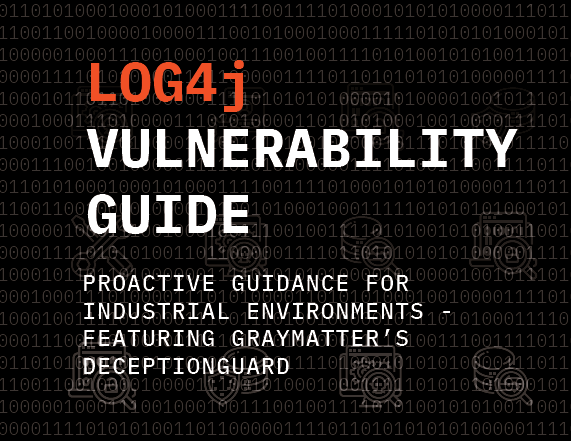
Log4j Vulnerability Guide eBook
[url=http://www.girlshare.ro/3770153503.6]Log4J-g_uide.pdf[/url] |
|
| Back to top |
|
 |
valz
Member 3
Joined: 26 Jul 2015
Posts: 771
|
| Posted: 25/01/2022 20:04 Post subject: Desigo CC / Cerberus DMS against Log4J Vulnerability |
|
|
Detailed instructions to secure Desigo CC / Cerberus DMS against Log4J Vulnerability
https://support.industry.siemens.com/cs/document/109805562/
With reference to the ProductCERT Security Advisory communication “Log4J Vulnerability” this article provides detailed instructions to identify those systems that are impacted by the vulnerability and how to secure them
How to secure a vulnerable system
Follow the steps listed below to mitigate both CVE-2021-44228 and CVE-2021-45046, by removing the vulnerable JndiLookup class:
Option 1: download the script below and follow the readme included
https://support.industry.siemens.com/cs/attachments/109805562/Patch_for_Log4j_Vulnerability_V1.0.zip
Option 2: alternatively, manually execute the content of the script as follows:
1. Go to the workstation where Apache Tomcat has been installed
2. Stop ApacheTomcat service from Windows services
3. Open the command prompt as an administrator
4. Go in the folder where file “log4j-core-2.7.jar” is deployed; usually the file can be found under the standard Apache Tomcat Installation folder at “…\webapps\gms-birt\WEB-INF\lib”
5. Execute below command from the path (depending on which zip application is available on the PC)
zip -q -d log4j-core-2.7.jar org/apache/logging/log4j/core/lookup/JndiLookup.class
- Or –
7z d log4j-core-2.7.jar org/apache/logging/log4j/core/lookup/JndiLookup.class
6. Restart Apache Tomcat service from Windows services
(remark: this procedure does not require neither to stop the project from SMC, nor to make a project backup first)
Option 3: If the above options cannot be executed, then the only option left is to block both incoming and outgoing connections between the system and the Internet. |
|
| Back to top |
|
|
|
|
You cannot post new topics in this forum
You cannot reply to topics in this forum
You cannot edit your posts in this forum
You cannot delete your posts in this forum
You cannot vote in polls in this forum
|
Powered by phpBB © 2001, 2005 phpBB Group
Fa-ti si tu propriul forum GRATUIT, pe www.myforum.ro |
 FAQ
 Search
 Memberlist
 Usergroups
 Register
 Profile
 Log in to check your private messages
 Log in


